

Somewhere in Asia right now, a payment is clearing every security check a bank has in place. The login is legitimate, the device is the one the customer uses, and the person tapping “confirm” is the genuine account holder, doing what a scammer on the other end of the line told them to do.
That scenario framed a recent webinar on fintech fraud prevention in Asia, where four leaders traced how the threat has shifted and what fintechs and financial institutions alike can do about it.
The numbers behind it are large and worrying. LexisNexis Risk Solutions analysed 116.1 billion transactions for its 2026 Global Cybercrime Report.
Its findings highlighted that automated bot attacks jumped 59%, and critically, the bots no longer sound robotic.

Fraudsters have trained them to mimic human behaviour closely enough to slip past the defences built to catch them. Attacks on existing accounts climbed faster still, with the login attack rate up 89% YoY.

Authentication can surely prove a customer pressed the button, but sadly, it cannot prove they understood what they were agreeing to.
The losses are vast, with Interpol calculating global fraud losses at an estimated $442 billion in 2025, ranking financial fraud among the top five global crime threats.
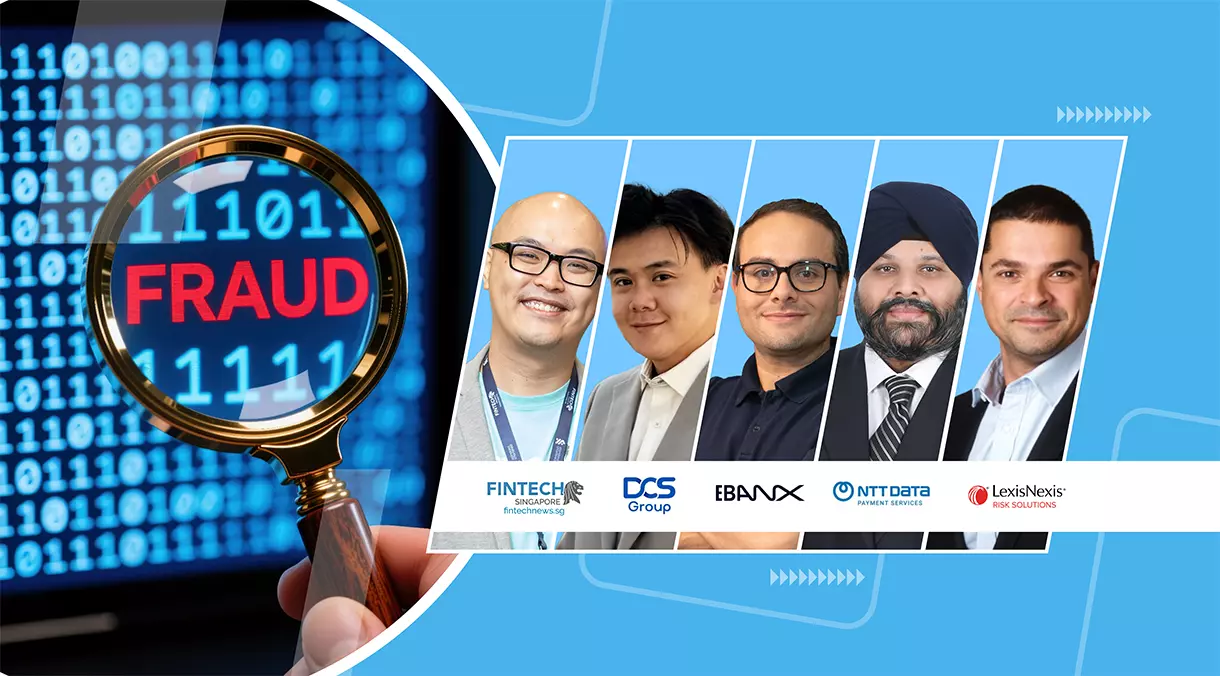
That reality set the tone at “Asia’s Multi-Billion-Dollar Fraud Crisis: Can Fintechs Still Build Trust?” webinar, hosted by Fintech News Network and sponsored by LexisNexis Risk Solutions.
The panel comprised Christopher Foye, Senior Director, Platforms, LexisNexis Risk Solutions; ChunHou Kok, Group General Counsel at DCS Group; Eduardo de Abreu, the Chief Product Officer of EBANX and CEO of EBANX Singapore; and Khushwant Singh, the Group Chief Risk & Credit Officer of NTT DATA Payment Services.
Moderated by Vincent Fong, Chief Editor of Fintech News Network, the panellists traded views on why the speed of fraud payments has outrun the speed of trust, and how financial institutions can protect customers without burying them in friction.
Fraudsters Have Stopped Aiming for the Front Door
When the discussion turned to how the threat landscape had evolved over the year, Christopher Foye, the Senior Director of Platforms at LexisNexis Risk Solutions, shared insights from the cybercrime report, where automated bot attacks spiked by 59%.
According to him, a couple of years back, these attacks were easy to spot. Now fraudsters are engineering them to imitate actual people, slipping past the defences organisations have built.

“Fraudsters are realising they need to simulate human behaviour to get past the controls organisations rely on,” he shared.
That same instinct is feeding the move towards agentic commerce, where attackers use AI to reproduce more of the customer workflow while still passing as human.
Chris flagged a second, less obvious shift: a rise in browser-based attacks. Most firms went mobile-first and concentrated on app security, leaving the browser comparatively unwatched. Pointing AI tools at a browser is also easier than aiming them at a mobile app, which may be pulling attacks back to that channel.
He explained that fraud no longer sits at one single point in the customer’s journey. From account openings and logins to password resets and payment initiations, fraudsters probe every one for a way in. For example, the login attack rate alone nearly doubled, up 89% YoY.
“Fraudsters aren’t just trying to get in through the front door. They’re attacking your existing accounts as well.”
The conclusion he drew is that digital adoption and fraud sophistication are climbing together, and the job is to add the controls that stop it without loading friction onto customers, who can take their business elsewhere in a tap.
Fraud Signals Mean Different Things to Different Merchants
When asked about where the balance between friction and fintech fraud prevention in Asia is hardest to strike, Eduardo de Abreu, the Chief Product Officer of EBANX and CEO of EBANX Singapore, pointed to e-commerce, where checkouts are tuned for every click, and any extra step feeds straight into conversion and the merchant’s bottom line.
His clients span very different verticals, with Shopee, Shein, PlayStation and Uber among them. That range is precisely why a single fraud threshold cannot work across the board. Customer behaviour differs by vertical, and so does what should count as suspicious.

“A behaviour that looks like a bot attack for a SaaS business can be the standard for a gaming platform when there’s a major release,” Eduardo shared.
The answer starts with agreeing, merchant by merchant, what normal looks like in each vertical, then setting thresholds with the payment processor to match.
Alignment cannot stop at the merchant, though. It has to run downstream to the acquirers and the issuers, so every party in the chain holds the same read on what is expected and what is about to happen in the days ahead.
To get there, his team consolidates more than 100 data points into a single view of behaviour that all sides can share and discuss.
“Once you align every party in the process, you can start to optimise each step of the funnel and deliver the best result, in a way everyone can trust.”
Only with that shared picture, he explained, can a merchant tighten controls at one point in the funnel without dragging down the checkout at the next.
Fraudsters Iterate in a Day, But Regulated Banks Can’t Do That
ChunHou Kok, Group General Counsel at DCS Group, spoke about how speed separates fraudsters from financial institutions.
Scammers can change tactics almost overnight, he said. They could move from chatbots engineered to make victims fall in love one week, to deepfakes of public figures soliciting money next.
Scammers had the leverage to test, iterate, and discard whatever fails, almost at will.
“Fraudsters evolve and iterate very fast. Financial institutions are constrained by governance and risk assessment requirements,” he shared.
Banks are not able to function at the same speed and format. Kok pointed to the MAS Guidelines on AI Risk Management, issued for consultation late last year, which will set expectations for how financial institutions govern and risk-assess their AI once in force.
AI used for data aggregation, collection or analysis sits at the lower-risk end. Meanwhile, AI embedded in deterministic controls such as transaction monitoring cannot simply be left to run on its own.
Liability tightens the constraint further. For example, while financial institutions carry the duty to freeze funds and accounts, they also owe customers a clear explanation for those actions.
On agentic payments, Kok called it one of the hottest topics in the payments world, turning on how to identify a payment agent in the first place. Both Visa and Mastercard are building infrastructure for trusted, agent-initiated transactions, he said, with pilot transactions already tested in Singapore.
“Do we have sufficient rules and governance right now? Not really. But we are getting there.”
No System Survives a Single Clicked Link
Returning to the human element, Khushwant Singh, the Group Chief Risk & Credit Officer of NTT DATA Payment Services, explained that fraud only succeeds when it finds the weakest link, and that link is almost always a person rather than a platform.
The best systems, the best technology, behavioural tools and analytics all account for little, he said, if the human on the other end clicks the wrong thing.

“We can have the best systems and the best technology out there, but if the human link isn’t addressed, the fraud still gets through,” Khushwant shared.
He pointed to a local report he had read days earlier: a finance employee at a large company whose phone was compromised, letting a fraudster send a WhatsApp message to the authorised signatory. The payment went through, and a sizeable sum left the business.
Scammers concentrate on the people least equipped to spot them, he added, targeting customers who are new to a bank or a company and older individuals who are less digitally savvy. A thin digital footprint makes them easier to deceive, and one link can be enough to let malware in and money out.
Education remains the priority, but he credited the banking and payments world with a genuine advance in AI-driven behavioural analytics.
Picking up a point raised earlier by fellow panellists, he noted that when a transaction sits well outside a customer’s usual pattern, the onus falls on the bank to step in, whether through an enhanced token or a fresh authentication challenge.
Some banks now prompt for PIN details in a different format before releasing a payment, he said, one of several attempts to close the gap.
“It’s always a battle between us and them.”
Watch the full webinar on YouTube below for the complete discussion on how fintech fraud prevention in Asia needs to be addressed without burying customers in friction.
LexisNexis RiskNarrative® brings powerful automation under your total control, uniting fraud detection, financial crime prevention, compliance and risk management across the entire customer lifecycle.
Request a Demo now! Risk Orchestration
Featured image edited by Fintech News Singapore based on an image by stocksbuddy on Magnific
